Anthropic opens its most powerful cyber models to more security teams under a three-tier program
Anthropic has merged Project Glasswing and its Cyber Verification Program into an expanded three-tier scheme giving vetted defenders access to Claude Opus 5.5, Sonnet 5.5 and Mythos 5.1 with reduced safeguards.
Anthropic on October 6 announced an expanded version of its Cyber Verification Program (CVP), which lets vetted cybersecurity professionals use its most powerful AI models with fewer safeguards, the company said in an official post. Every tier of the revamped program includes access to Claude Opus 5.5, Claude Sonnet 5.5, Claude Mythos 5.1 and future models.
For the past six months Anthropic has run two separate programs: Project Glasswing, which gave organizations securing the most critical software access to Claude Mythos, its most cyber-capable model family, and the original CVP, which gave vetted security teams reduced safeguards on Claude Opus and Sonnet models. The two are now combined into a single offering.
The new program has three tiers, each with its own verification requirements and security controls. Defense Access covers work such as security operations, incident response, malware reverse-engineering and vulnerability validation, and is open to corporate, university and government security teams, critical-infrastructure operators such as regional hospitals and municipal utilities, open-source maintainers and researchers with a record of reported vulnerabilities. Red Team Access adds authorized penetration testing and red-teaming, and only organizations can apply. Specialized Access, which has the fewest cyber blocks, is reserved for a limited set of organizations authorized to test safety-critical systems such as flight operating systems, power grids, telecom networks and interbank transfer infrastructure; Anthropic reviews each of them in collaboration with the US government, and existing Glasswing members move into this tier.
According to Anthropic, Glasswing partners found at least 129,000 verified software vulnerabilities between April and July 2026, and the company’s own open-source scanning found 5,500 more between April and October. More than 33,000 have so far been rated critical or high severity. As Reuters reported, Anthropic says the figures are likely an undercount based on a limited survey of partners and expects the true impact to be at least five times higher.
Anthropic said it tested the tiers on the CyScenarioBench evaluation: without CVP access every task was blocked on the first prompt; in the Defense Access tier 46 of 50 trials were blocked at some point; and in the Red Team Access tier no blocks occurred, with Claude Opus 5.5 completing 34 of 50 tasks. Enrolled organizations must allow data retention so Anthropic can monitor for misuse, until a new Enterprise Frontier Safeguards option arrives later this fall. CVP is available on the Claude Platform, Google Cloud’s Vertex AI and Microsoft Foundry.
Reuters noted that Anthropic’s April unveiling of Claude Mythos Preview had raised fears that AI could hack software before it had been secured.
Related articles
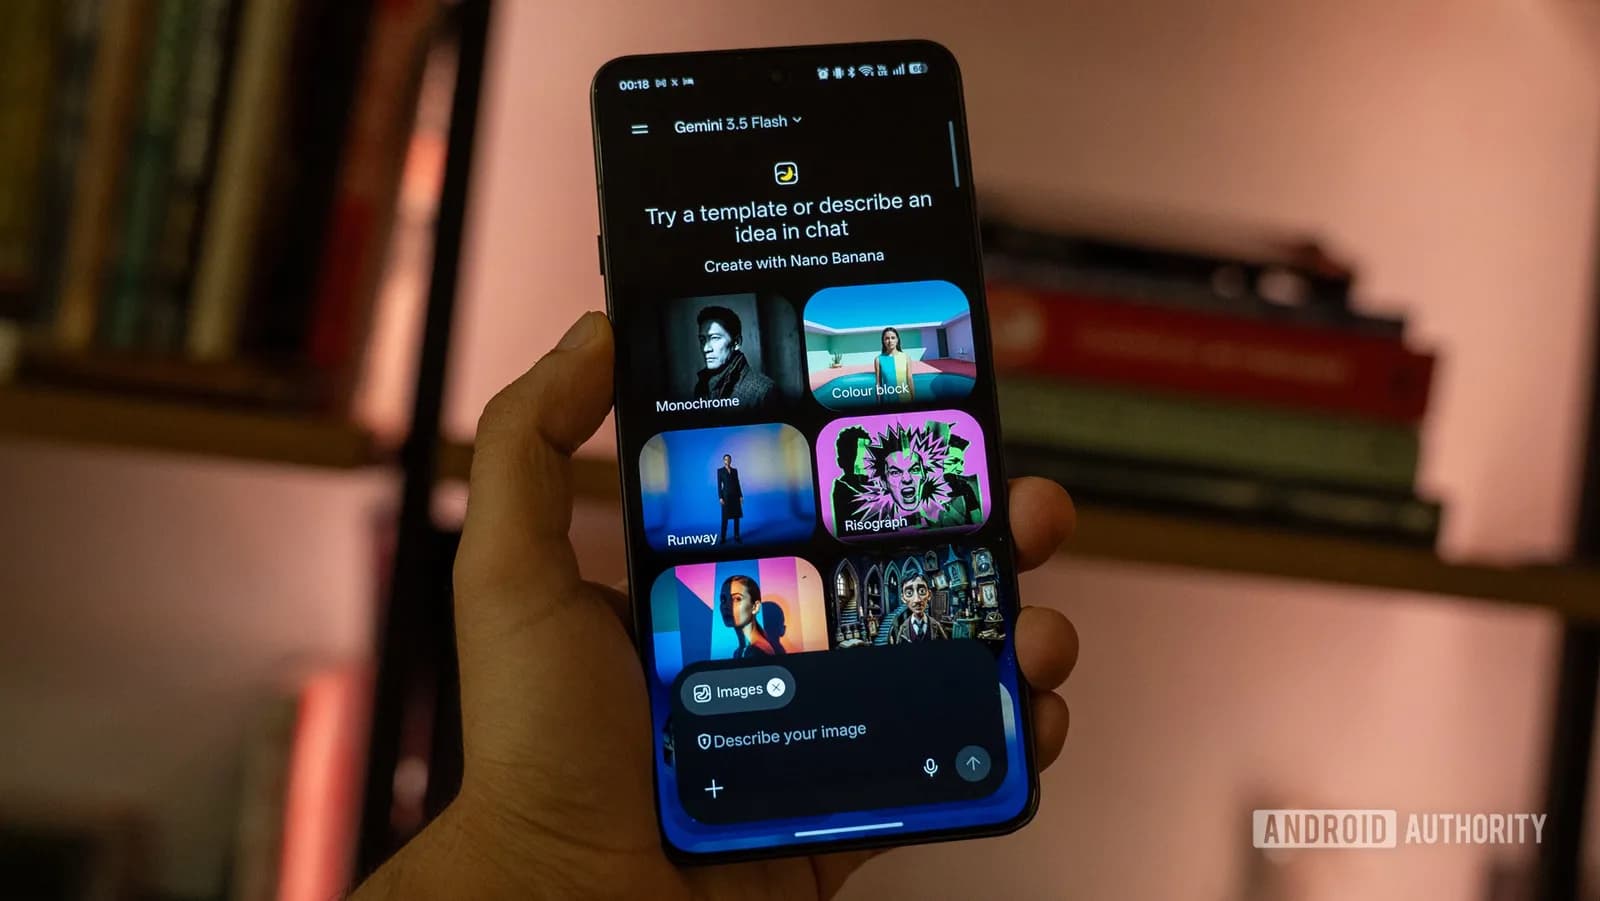
Google launches Nano Banana 2.1 with better visuals, editing—and half the image cost
On October 6, 2026 Google released Nano Banana 2.1, a Gemini 3.6 Flash–based image generation and conversational editing model rolling out across Gemini, AI Mode, AI Studio and the Gemini API, with paid-tier image output priced at roughly half of Nano Banana 2.

OpenAI drops another batch of mathematical breakthroughs
OpenAI has revealed solutions to a number of long-standing mathematics problems produced by an unreleased frontier model in a batch of 722 manuscripts, covering 372 result families that group related…
Tiny light-measuring chip helps stabilize 10× more combs, could shrink atomic clocks
Researchers have demonstrated a chip-based optical frequency comb that matched bulky tabletop systems in key...
OpenAI’s largest mathematics release tackles 4,000 problems with Lean-checked proofs
OpenAI has released a large collection of mathematical research produced by an internal frontier model,...
85-kW MARVEL microreactor gets liquid-metal coolant ahead of criticality test
A small nuclear reactor at Idaho National Laboratory is approaching its first criticality test after...