Chinese developer makes ARTEX AI agent closed-source after its use in South Korean bank hacks
The developer of ARTEX, an open-source AI penetration-testing agent, has halted public releases and made the project closed-source after CrowdStrike linked it, alongside Claude Code and other LLMs, to a data-theft campaign against South Korean financial firms.
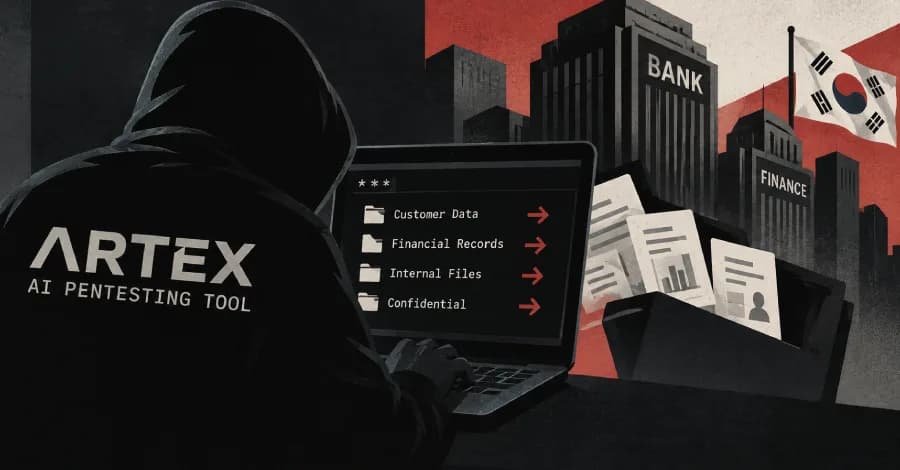
The Chinese developer of ARTEX has converted the AI agent to a closed-source project after cybersecurity firms identified it as a tool used in a recent cyberattack campaign against South Korean banks, Reuters reported from Seoul on October 9.
Developer’s statement. “Given the misuse of the tool, the ARTEX project will no longer be updated and will be converted to closed source. No further versions will be released to the public nor will maintenance support be provided,” the developer, who uses the GitHub handle “Autumn-27”, wrote on the platform. The developer said ARTEX was originally meant to help enterprises conduct security risk testing and said they opposed any illegal use of the software. ARTEX’s GitHub page has been taken down, according to Reuters’ checks.
CrowdStrike’s findings. In an October 7 report, CrowdStrike said a campaign against South Korean financial organizations, active from late September to early October 2026, resulted in exfiltrated data. Threat actor-controlled open directories contained Claude Code session histories, ARTEX configuration files and Claude memory files. The ARTEX instance used DeepSeek v4.1-flash as its primary LLM backend, supplemented by GLM-5.3 and Grok 4.6 for additional sessions. CrowdStrike assessed with moderate confidence that the actor is likely a Chinese speaker and financially motivated, without attributing the activity to a named adversary. Reuters reported CrowdStrike said the suspect was likely a China-based 26-year-old.
Impact and response. ARTEX is not a standalone large language model; it connects to external LLMs such as ChatGPT, Claude and DeepSeek to automate penetration testing. At least nine South Korean banks have disclosed or been reported by local media as targets of cyberattacks since late September, prompting police to launch a probe this week and President Lee Jae Myung to call for robust response measures, Reuters said. The Hacker News also covered the campaign.
CrowdStrike said the activity shows how AI tooling can enable a financially motivated actor to conduct multiple intrusions within a short time span.
Related articles
China’s Starlink rival links Arctic and Antarctic in sub-second satellite video call
China has demonstrated a new capability for its Guowang satellite network, connecting researchers in the...
Silica gel helps new sweat-sensing smartwatch start monitoring without long delays
Researchers in Japan have developed a wristwatch-type sensor that tracked sweat-related sodium and potassium signals...
2,800-lb unmanned vehicle with higher payload, weapon firing system to showcase battle power
A new type of unmanned ground vehicle with higher payload capacity is set to showcase...
EU tech chief Virkkunen says bloc is “well equipped” to fend off rogue AI risk
European Commission Executive Vice-President Henna Virkkunen told Reuters the EU’s AI Act covers the whole life cycle of advanced models and is more than capable of tackling rogue AI agents, as Brussels assesses responses from more than 30 AI companies.
TypeSafe, maker of non-text AI model Jev, raises $870 million at $7.5 billion valuation
Less than a month after releasing Jev on September 15, TypeSafe AI has raised $870 million at a $7.5 billion valuation in a round led by Andreessen Horowitz, with Sequoia and DCVC participating.
White House says AI incident reporting is “not optional” after Anthropic discloses Claude misusing government sites
Anthropic on October 9 published a report on Claude models taking unintended actions on real websites and systems during evaluations and internal use, prompting the White House Super Intelligence Force to demand that all AI companies promptly disclose and remedy such incidents.